 JIGSTACK
#projects · Developer security
Safeship.
A security co-pilot for people who build with AI tools. Connect a GitHub repo and it finds leaked secrets, insecure code, and vulnerable dependencies, then explains each fix in plain English.
- Year
- 2026
- Platforms
- Web
- Users
- 20+
- Type
- Web + AI
Overview
Safeship is a security co-pilot for people who build with AI tools. Connect a GitHub repository and it scans the code for leaked secrets, insecure patterns, and vulnerable dependencies, then explains every finding in plain English, ranked by real-world risk, with a copy-paste fix.
Scans run on on-demand GitHub Actions runners with gitleaks, Semgrep, and OSV-Scanner. Secrets are redacted before anything leaves the runner, and the cloned code is destroyed when the job ends. It is static analysis only: Safeship never probes or sends traffic to live systems.
Key features
- Secret, code (SAST), and dependency scanning in a single run
- Plain-English explanations and a 0–100 safety score for every scan
- Fix with AI: opens a pull request that resolves a finding
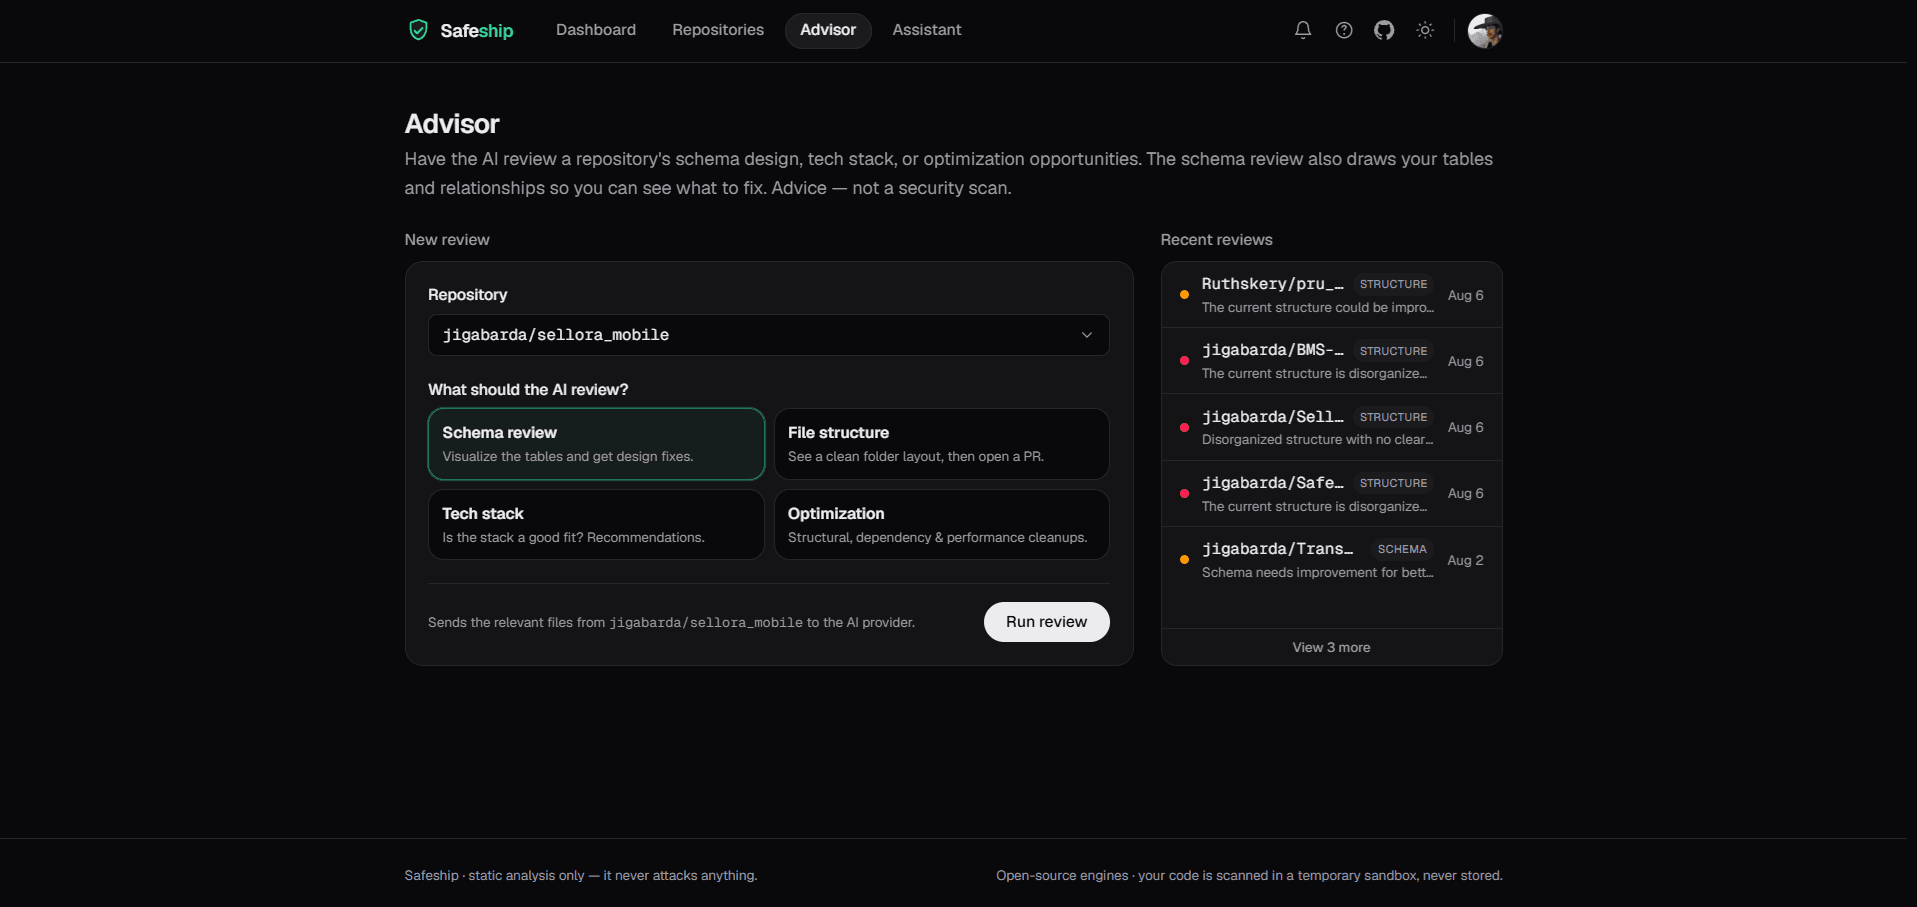
- Advisor reviews a repo's schema, tech stack, and structure, and draws its tables
- Assistant chat for security and code questions
- Runs on Groq in the cloud or fully local with Ollama